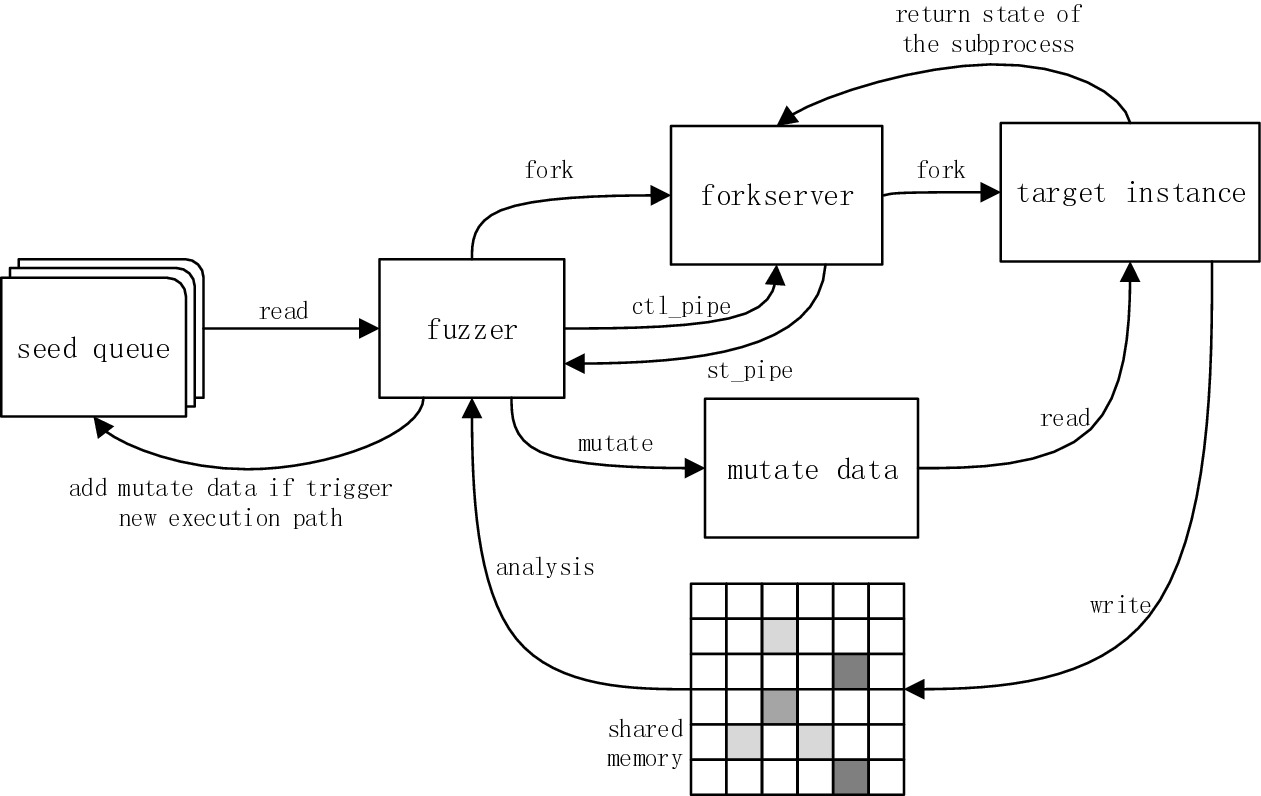
afl-fuzz 框架
afl-fuzz 的整体架构,新手理解起来还是比较费劲,网络上发现一张图觉得不错,放上来大家看看,感谢原作者。
本博客所有文章除特别声明外,均采用 CC BY-NC-SA 4.0 许可协议。转载请注明来源 安全代码!
相关推荐
2024-04-01
AFL++ 漏洞挖掘实例
☆ 1. 模糊测试工具 AFL / AFL++介绍模糊测试是一种黑盒测试方法,它通过向软件输入随机或异常的数据,来触发软件中的错误或异常。AFL 是 Google 开发的一款 fuzz 工具,它最初由 Michal Zalewski 开发,被设计为一种模糊测试工具,用于自动发现程序中的漏洞。 在 AFL 之前,模糊测试工具大多采用随机生成输入数据的方法。这种方法虽然简单,但效率低下,很难发现软件中的隐藏路径。AFL 引入了覆盖率导向的模糊测试方法,它会根据软件的执行路径来优化输入数据。这种方法可以有效地提高模糊测试的效率,并更容易发现软件中的隐藏路径。 AFL 的发布,标志着模糊测试工具进入了新的时代。AFL 的成功,激发了许多其他研究人员和开发人员对模糊测试工具的改进和研究。它对软件安全领域产生了深远的影响。AFL 的成功,证明了模糊测试是一种有效的软件安全测试方法。 AFL 在模糊测试工具发展史上的具体贡献主要有:1)开创了覆盖率导向模糊测试的新时代2)极大地提高了模糊测试的效率和效果3)激发了其他研究人员和开发人员对模糊测试工具的改进和研究 AFL作为一款开创性的...
2016-06-08
PowerPoint 彩蛋和加密
PowerPoint的彩蛋PowerPoint的彩蛋是一个很复杂的密码 /01Hannes Ruescher/01 发现这个密码是在 binvul的论坛里面,在网上搜索了一下有几个链接提到了这个密码。 http://social.msdn.microsoft.com/Forums/en-US/4194b097-c5ca-416a-b9d6-7a65ff7d9d43http://msdn.microsoft.com/en-us/library/dd923811(v=office.12).aspx 第二个链接里面有一段关键的内容, 1234If the user has not supplied an encryption password and the document is encrypted, the default encryption choice using the techniques specified in section 2.3 MUST be the following password: "\x2f\x30\x31\x48\x6...
2023-09-06
Android WebView 漏洞
☆ 来自 developer.android.com 的信息Android 官方网站对addJavascriptInterface的介绍如下: 123456789101112public void addJavascriptInterface (Object object, String name) Added in API level 1Injects the supplied Java object into this WebView. The object is injected intothe JavaScript context of the main frame, using the supplied name. This allows the Java object's methods to be accessed from JavaScript. For applicationstargeted to API level JELLY_BEAN_MR1 and above, only public methods that are annotated w...
2023-09-06
llvm Coverage 可视化
Google 提供的工具Google 提供了一个工具 https://cs.chromium.org/chromium/src/tools/code_coverage/coverage.py 12345678$ gn gen out/coverage \ --args='use_clang_coverage=true is_component_build=false dcheck_always_on=true'$ python tools/code_coverage/coverage.py \ crypto_unittests url_unittests \ -b out/coverage -o out/report \ -c 'out/coverage/crypto_unittests' \ -c 'out/coverage/url_unittests --gtest_filter=URLParser.PathURL' \ -f url/ -f crypto/ 一些参数的含义: 1...
2023-09-06
onefuzz 简单分析
deploy agent (部署)123unzip onefuzz-deployment-$VERSION.zippip install -r requirements.txt./deploy.py $REGION $RESOURCE_GROUP_NAME $ONEFUZZ_INSTANCE_NAME $CONTACT_EMAIL_ADDRESS Azure CLI logged in 后,执行上面命令可以在 Azure 上部署 agent 需要订阅 Azure, 可能要收费 安装 onefuzz CLI123wget https://github.com/microsoft/onefuzz/releases/download/1.0.0/onefuzz-1.0.0-py3-none-any.whlwget https://github.com/microsoft/onefuzz/releases/download/1.0.0/onefuzztypes-1.0.0-py3-none-any.whlpip install ./onefuzz*.whl 执行 fuzz 任务1on...
2023-09-06
恢复 Android App 的截屏功能
今天遇上某 App 禁止截屏,其实就是使用了下面这段代码 1getWindow().setFlags(LayoutParams.FLAG_SECURE, LayoutParams.FLAG_SECURE); 使用 frida 脚本可以绕过绕过这个限制 (使用 frida 需要将手机 root)。 12345678910111213Java.perform(function () { // https://developer.android.com/reference/android/view/WindowManager.LayoutParams.html#FLAG_SECURE var FLAG_SECURE = 0x2000; var Window = Java.use("android.view.Window"); var setFlags = Window.setFlags; //.overload("int", "int") setFlags.implementation = ...